CompTIA CySA+ is worth it if you work, or plan to work, in security operations, vulnerability management or incident response and already have Security+ level knowledge. The current version is V4 (CS0-004), launched in June 2026; the English CS0-003 exam retires on 22 December 2026. Here is what the exam involves and how it compares.
CS0-003 or CS0-004: which one you will sit
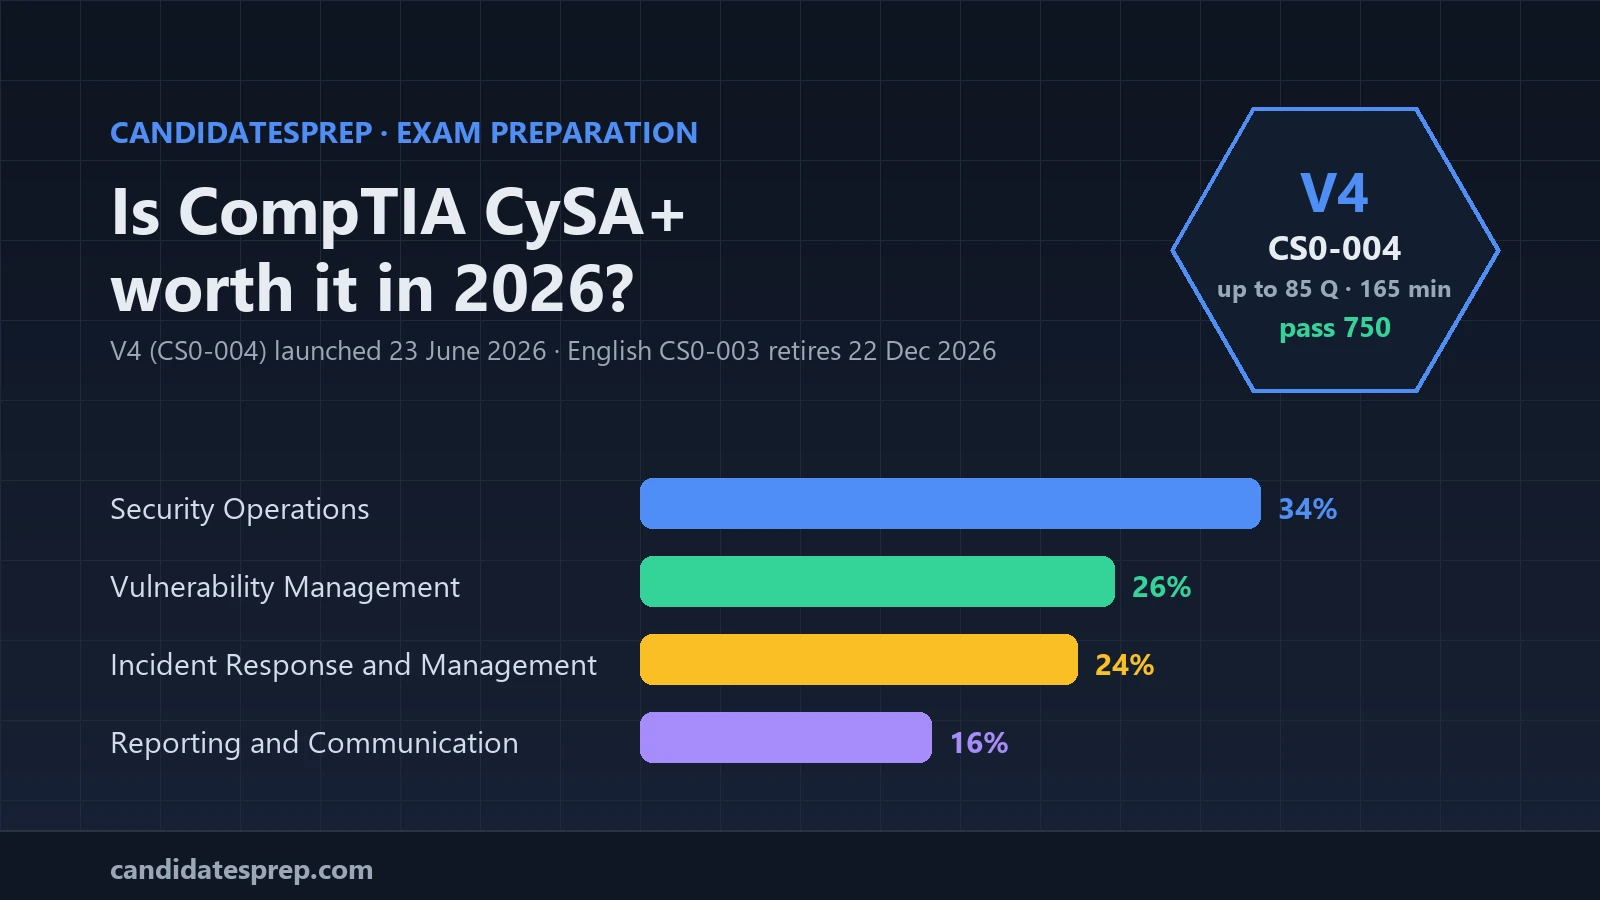
CompTIA refreshed CySA+ this year. V4, exam code CS0-004, launched on 23 June 2026. CS0-003 is now listed as the retiring version: its English learning products retire on 22 November 2026 and the English exam on 22 December 2026, with the Japanese, Portuguese and Spanish versions following on 23 March 2027.
If you are deep into CS0-003 preparation and can sit before December, finishing on that version is reasonable. If you are starting now, prepare for CS0-004, because that is the version new study material is written for.
What the CS0-004 exam looks like
According to CompTIA:
- A maximum of 85 questions, mixing multiple-choice and performance-based questions.
- 165 minutes.
- A passing score of 750 on a scale of 100 to 900.
- English at launch, with French, Japanese, Spanish and Portuguese listed as coming soon.
Performance-based questions put you in a simulated task rather than a single-answer prompt, and they can eat your time. Our guide to Security+ performance-based questions covers how to approach that format, and the same habits carry over.
The four domains and what changed
V4 keeps the four domains of CS0-003 but shifts the balance:
- Security Operations: 34% (33% in CS0-003)
- Vulnerability Management: 26% (30%)
- Incident Response and Management: 24% (20%)
- Reporting and Communication: 16% (17%)
Incident response gains weight and vulnerability management loses some. CompTIA's V4 FAQ lists the main content changes: dedicated coverage of AI use cases, risks and governance; AI-assisted SOC workflows; expanded EPSS-based vulnerability prioritisation; more on zero trust network access and SASE; and stronger coverage of software bills of materials and supply chain risk. Cloud and hybrid environments also run through the objectives. Older CS0-003 notes will cover most of the ground, but not these topics.
Who CySA+ suits, and who should wait
CompTIA recommends about four years of experience in a SOC analyst or vulnerability analyst role. That is a recommendation rather than an entry requirement, but it signals the level: the exam expects you to apply security concepts to alerts, scans and incidents, not just define them. CompTIA links it to roles such as security analyst, SOC analyst, vulnerability analyst, threat intelligence analyst and incident responder.
It is a strong fit if you already do monitoring, triage or vulnerability work and want vendor-neutral proof of it. If you are new to security, start with Security+; our Security+ SY0-701 guide sets out how to pass it.
Where it sits next to Security+ and other analyst certs
CompTIA describes Security+ as foundational and CySA+ as intermediate: Security+ shows you understand security concepts, while CySA+ shows you can apply them in operational environments. In CompTIA's hierarchy, CySA+ sits level with PenTest+, its offensive counterpart, and below SecurityX.
Outside CompTIA, the usual alternatives are:
- Microsoft SC-200 (Security Operations Analyst Associate), built around Microsoft Sentinel and Defender and renewed every 12 months through a free online assessment.
- GIAC GCIH, a practitioner certification in incident handling that uses hands-on CyberLive lab questions.
- CISSP, a broader and more senior credential that suits people moving towards security leadership.
CySA+'s advantage is that it is vendor-neutral, so the skills transfer across SIEM platforms. If your employer runs on one vendor's stack, adding that vendor's exam later can make sense.
Cost, renewal and the extras
CompTIA lists the US retail voucher at $425; prices vary by country. CySA+ is valid for three years and renews with 60 continuing education units, by passing the latest version of the exam, or by earning a qualifying higher certification. Because CompTIA renews lower certifications with higher ones, holding CySA+ also keeps Security+ current. CompTIA also lists CySA+ as approved under the US DoD's 8140.03M directive, which matters for many US government and contractor roles.
Dates, prices and objectives change, so check CompTIA's CySA+ V4 page for current details before you book.
Practise under real exam conditions
A 165-minute exam with performance-based questions rewards pacing as much as knowledge. Sit full, timed mocks that mirror the real exam's timer, navigation and flagging, practise flagging a long task and coming back to it, then use results broken down by topic to see which of the four domains is costing you marks. Trainers running security cohorts can see how IT and cloud training providers track readiness across a group.
The bottom line
CySA+ is worth it if your work is, or soon will be, monitoring, vulnerability management and incident response, and you want a vendor-neutral credential that also keeps Security+ current. Prepare for CS0-004 unless you can sit CS0-003 before 22 December 2026.
Rehearse the timing with a full mock on the CandidatesPrep simulator, or book a demo to run CySA+ practice for a whole cohort.